AI coding agents
Developer agents that run commands, edit code and call tools.
SaaviAIDR
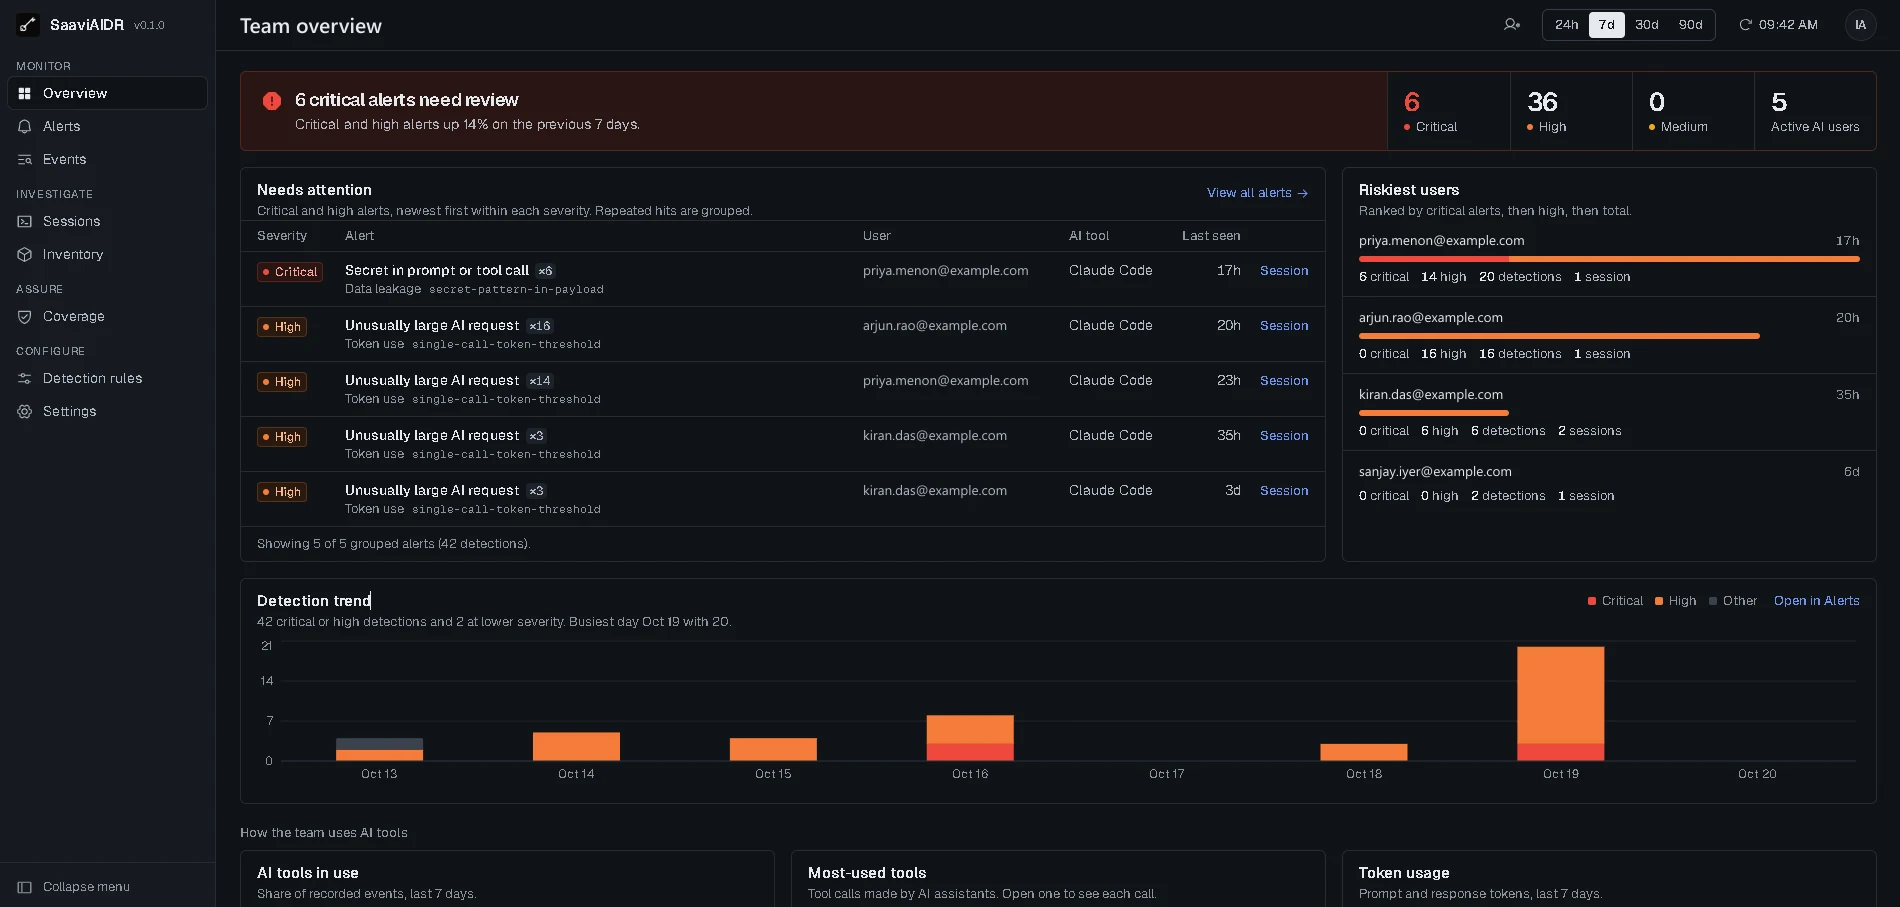
See what your AI agents and chatbots are doing, catch risky activity as it happens, and respond before it becomes an incident.
Developer agents that run commands, edit code and call tools.
Internal assistants that work with company data.
Public-facing assistants that speak for your brand.
Workflows that act across your systems on their own.
Works with
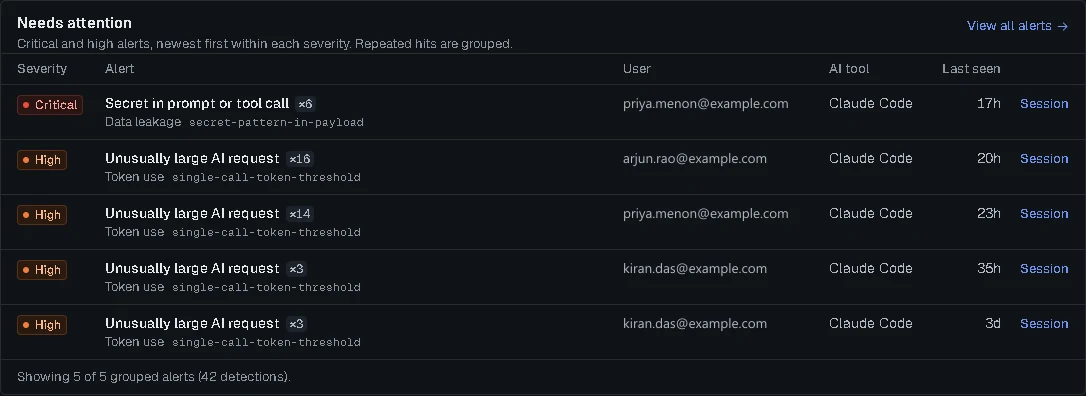
See which agents, models, MCP servers and users are active, and label each as approved or under review.
Prompts, responses, tool calls, files, model usage and cost, captured for every session.
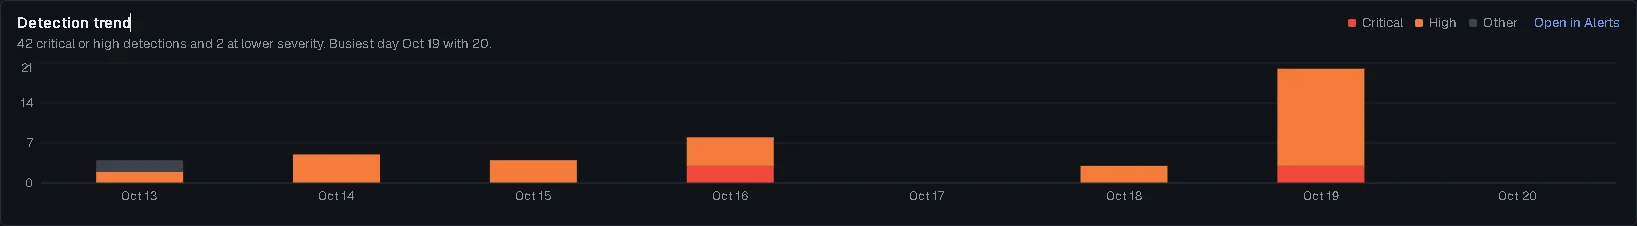
Built-in rules for prompt injection, jailbreaks, data leakage, secret-file access and destructive commands.
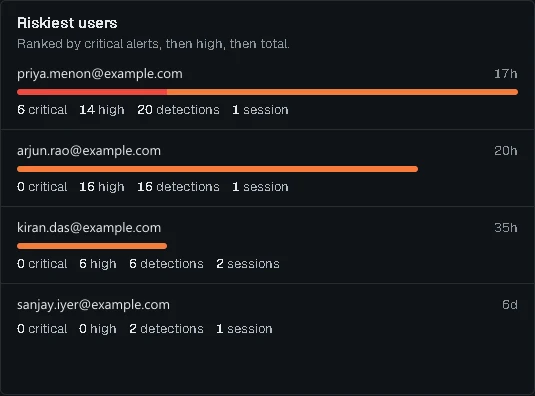
Baselines for each user and agent flag unusual tools, token spikes and changes in behaviour.
Each alert is reviewed with its session context and given a verdict, confidence level and likely intent.
Playbooks can end sessions, revoke keys or quarantine agents, and can be tested safely before they are enforced.
SaaviAIDR
01
Your AI agents and applications send activity data to SaaviAIDR.
02
All activity is converted into one consistent format.
03
Rules and behaviour analytics check every event in real time.
04
Alerts are analysed and response playbooks take action.
A clear picture of AI risk across the organisation.
Alerts, investigations and response in one place.
Visibility into which agents, models and tools are in use, and what they cost.
Self-hosted and single-tenant. Your AI activity data stays inside your environment.
Alert analysis can run on a local model, so no data leaves your environment.
Findings export to your existing SIEM and SOAR tools.
Separate roles for administrators, SOC managers and analysts, with prompt content masked for analysts.
Required on every sign-in.
Every configuration change is recorded.
Secrets and personal data are redacted.
We'll walk you through the platform and how it fits your environment.